

Key Takeaways:
- An access control system determines who can view, use, or modify systems, applications, and data, making it a core part of modern cybersecurity.
- Access control in cybersecurity is critical for preventing unauthorized users from accessing sensitive business information, especially in remote and hybrid work environments. It also helps reduce data breaches, limit insider threats, improve incident response, and support compliance.
- An effective access control system works through identification, authentication, authorization, and continuous monitoring to reduce unauthorized access and strengthen governance.
- Understanding the types of access control, such as RBAC, MAC, DAC, ABAC, break-glass, and rule-based access, helps you choose the right model for your organization’s risk, compliance, and collaboration needs.
If there is one fundamental security rule that all organizations should follow, it is that not everyone should have access to everything. Just as you lock your door to keep intruders out, businesses must establish clear and comprehensive security measures to protect against unauthorized access. In reality, that responsibility goes well beyond a basic lock and key.
Since work environments are no longer confined to the four walls of the office, with remote and hybrid arrangements in place, the number of ways data can be exposed, misused, or stolen has expanded.
In fact, Verizon’s 2026 Data Breach Investigations Report analyzed more than 22,000 confirmed breaches across 145 countries and found that credential abuse was involved in 39% of breaches when traced across the entire attack chain — not just the initial point of entry. In other words, once attackers get past the front door, weak access control is often what allows them to walk straight to the vault. For this reason, organizations must learn to expand and strengthen their security measures, and they must do it quickly.
It all starts with a robust access control system.
What is access control?
Access control is a process that restricts users’ access to systems, applications, and data based on company-defined rules or permissions. These permissions determine the level of access, which mostly depends on the user’s role and responsibility.
But it is not just about keeping outsiders out. Access control is also about making sure internal users or employees only have the level of access they need to do their jobs. Why does this distinction matter? It is mainly because many recorded security incidents do not come solely from external attackers. According to IBM, insider breaches cost organizations USD 4.99 million on average, showing how much damage internal misuse or abuse of access can cause.
Why is access control vital for security?
First and foremost, an established access control system prevents unauthorized users from entering systems or viewing sensitive information. Therefore, protecting the organization from potential risks. Apart from that, access control:
Reduces the risks of a breach
Many cyber incidents begin with compromised credentials or excessive permissions. If one account is stolen and that account has broad access, the damage can spread quickly. Access control reduces breach risk by limiting what an attacker can do even if they manage to get in. When access is segmented and aligned with actual responsibilities, one compromised account is less likely to expose the entire organization.
Supports compliance
Regulatory and governance frameworks like SOX and GDPR expect organizations to control and document access to sensitive data. While the exact requirements vary, the underlying principle is consistent: access should be limited, justified, and traceable.
An effective access control system supports compliance by helping you:
- Restrict access to confidential records
- Document who accessed what and when
- Review permission changes over time
- Show that sensitive information is handled responsibly
Limits insider threats
Insider threats can involve malicious intent, but they can also result from simple, unintentional mistakes, such as sending the wrong file, downloading sensitive information to an unsecured device, or retaining access after a role change.
Access control in cybersecurity limits insider risk by ensuring users have only the permissions they need. This reduces unnecessary exposure and makes it easier to spot behavior that falls outside normal patterns.
Improves incident response
When access activity is logged and monitored, your team can respond to security incidents faster and with more clarity. If unusual access occurs, logs can help you understand:
- Which account was used
- What systems or files were accessed
- When the activity happened
- Whether permissions were changed
- How far the activity spread
This visibility speeds up investigation and containment. It also helps leadership evaluate the impact of an incident and take corrective action with better information.
How does an access control system work?
While the specifics vary from one company to another, an access control system usually operates through these components:
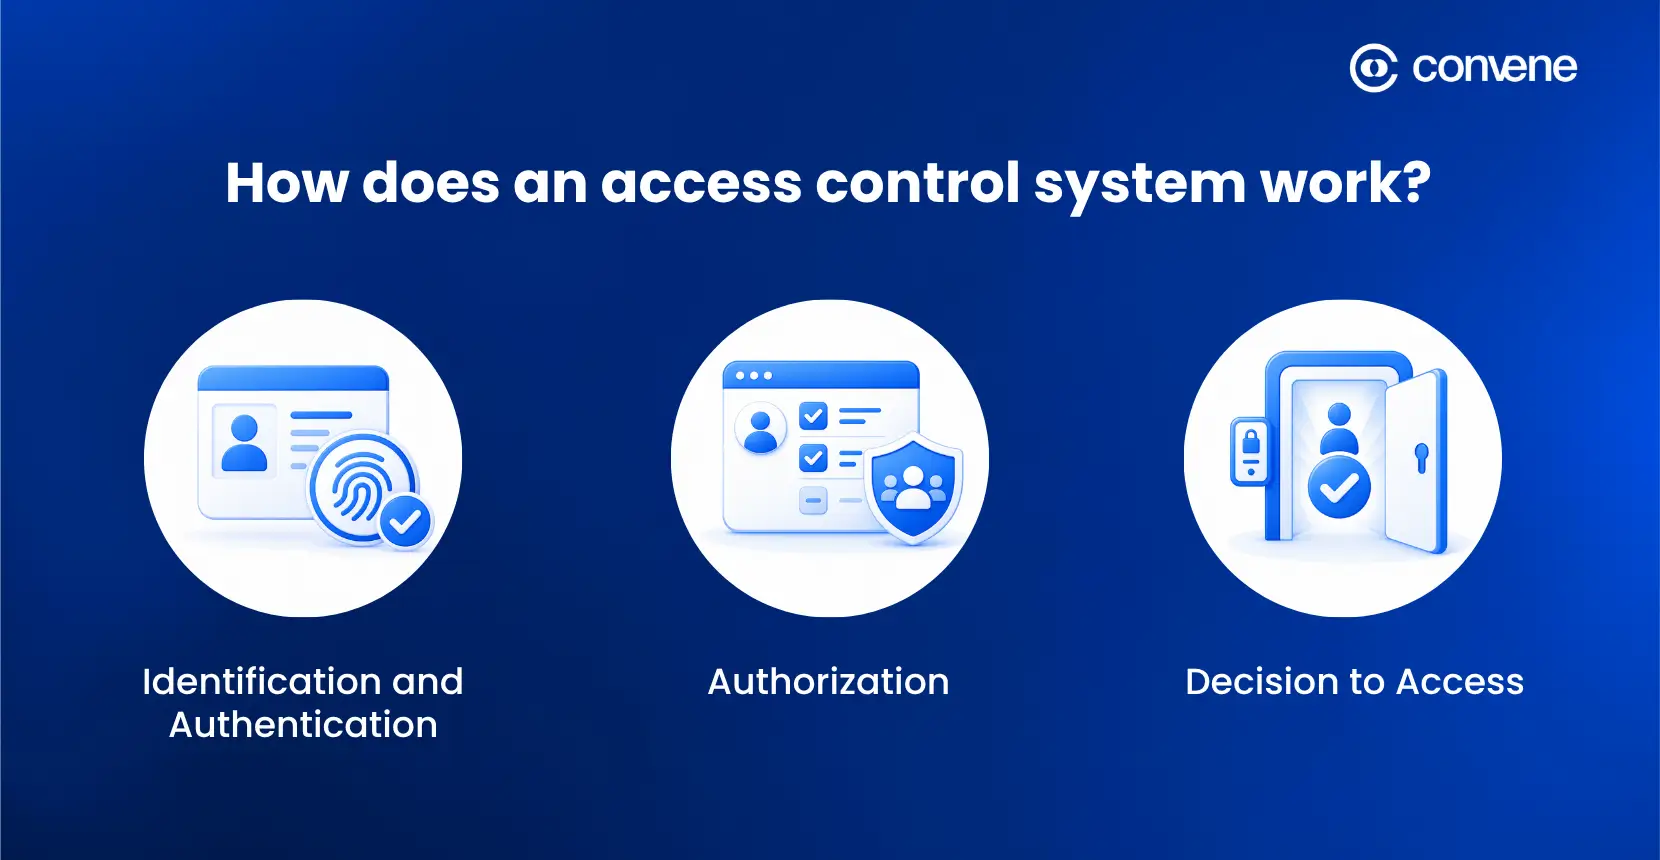
Identification and Authentication
The procedure starts when a user claims an identity with a username, email address, employee ID, or a security badge. Once the user identifies themselves, they must confirm their identity by presenting valid credentials. Typically, authentication requires one or more (for systems that use multifactor authentication or MFA) of the following factors:
- Knowledge, or something you know, like passwords, personal identification numbers (PINs), or answering a security question (your birthday, your mother’s name, or the name of your first pet, etc.)
- Possession, or something you have, such as a mobile device, hardware token, or smart card
- Inherence, or something you are, such as a fingerprint, facial scan, or voice command
Authorization
The system establishes user permissions upon successful authentication. Authorization determines the level of access a user may have, whether they can view a file, edit it, approve it, download it, or share it. This is an important aspect, as CEOs, board members, and secretaries could all require different privileges even when working on the same paper or platform.
Take, for example, a board secretary or administrator tasked with uploading and disseminating board packs but cannot review or approve documents, or an outside advisor given limited access to pertinent meeting materials but not to private board records.
Decision to Access
Based on the policies in place and the current setting, the system then makes an access decision: allow, deny, or limit access. For instance, if a login attempt appears risky due to an unfamiliar device or location, access may be blocked or escalated for additional verification.
What are the types of access control?
Selecting the appropriate access control model is not one-size-fits-all and usually relies on several factors, including company size and specific security needs. Here’s a list to get to know each access control category better:
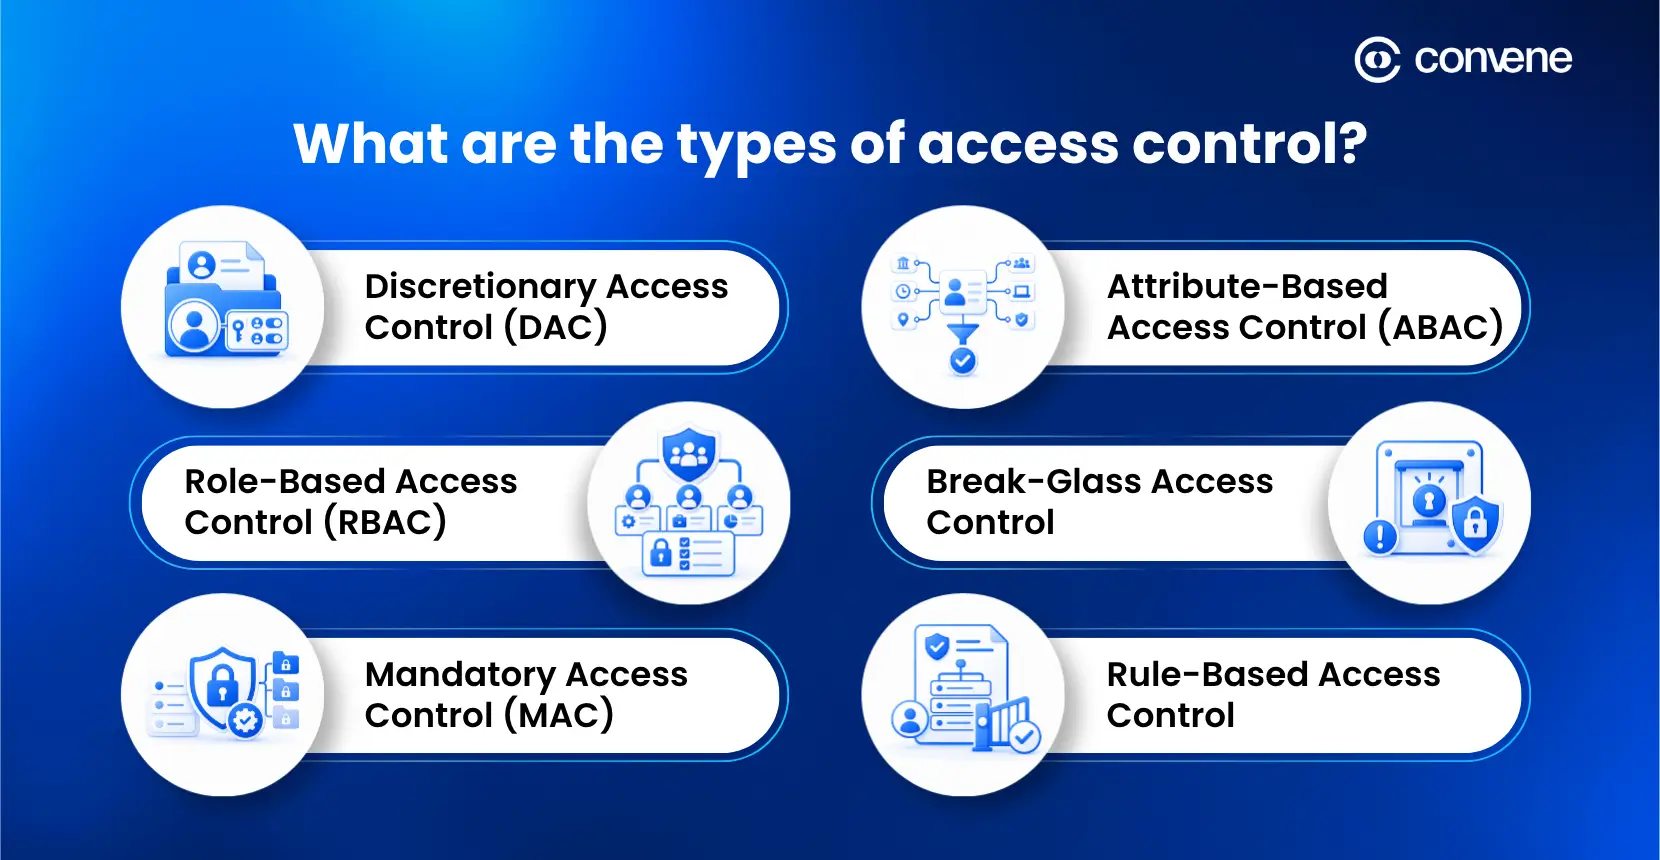
Discretionary Access Control (DAC)
Discretionary access control is when the owner of a resource chooses who has access to it. As the name suggests, it is up to the document owner to decide who can view, change, distribute, or manage a file and what level of access each user has.
DAC is flexible and simple to implement in collaborative contexts. But it also has the potential to be inconsistent if users offer access too broadly or without sufficient control. Too much discretion in businesses handling sensitive governance data might lead to unwarranted exposure.
Role-Based Access Control (RBAC)
Instead of setting access person by person, you define what each role can do and apply those permissions consistently.
RBAC works well when users with similar responsibilities need similar access. This strategy streamlines administration and facilitates governance, as access is based on job function, not personal preference. For example, an employee is given access to emails and other shared files, while IT personnel are given additional access to network settings and user accounts. RBAC is one of the most practical and scalable techniques of access control for many businesses.
Mandatory Access Control (MAC)
MAC is commonly used in environments that deal with extremely sensitive or regulated information, such as in the government, financial, and healthcare industries. It provides high security and centralized management of access rights, allowing enterprises to preserve sensitive information and comply with regulations. In a MAC setup, access is determined by a central authority according to stringent classification or clearance standards, so that users, no matter their position in the company, cannot override permissions. So, even if a high-ranking executive requests access to a specific file, they cannot do so unless given explicit clearance. However, this approach is less flexible and can be more complex to manage.
Attribute-Based Access Control (ABAC)
Unlike RBAC, attribute-based access control grants or restricts access based on attributes rather than roles. These traits can be:
- Department/seniority of the user
- Document’s classification level
- Device being used
- User location
- Access time
ABAC is particularly beneficial in companies where access decisions need to be more nuanced than what a static role can deliver. For example, an executive can access confidential board information only from a managed device and over a secure connection. This makes ABAC a great choice for enterprises that want to maintain security while enjoying flexible work arrangements.
Break-Glass Access Control
Break-glass access control is intended for emergency use. This enables authorized users to override usual restrictions temporarily when urgent action is needed, such as during a system outage, cyber incident, or medical or operational emergency.
This model is important because excessive rigidity in controls can slow down response when speed is most critical. However, break-glass access should be strictly controlled and heavily logged so it can’t be abused.
Rule-Based Access Control
Rule-based access control enforces pre-existing rules to decide access. These rules can apply to all users or specific scenarios, such as blocking access from certain locations, requiring stronger authentication for high-risk actions, or restricting access outside working hours.
This model is typically used alongside other techniques, such as RBAC or ABAC. It adds a layer of control by uniformly applying security policies across the enterprise.
How to Implement an Access Control System
Cybersecurity starts from the top, and for organizations, that means establishing clear rules around who can access what, why they need access, and how that access is monitored over time. To get started, here is a simple checklist:
- Identify sensitive resources: Determine which systems, applications, files, and information require access restrictions.
- Define user roles: Group users based on their responsibilities and determine what level of access each role requires.
- Apply the principle of least privilege: This principle simply means giving users only the access they need to perform their responsibilities.
- Establish authentication requirements: Use strong passwords, MFA, and other appropriate authentication measures.
- Set access permissions: Configure role-based or attribute-based permissions to control access to specific resources.
- Review access regularly: Periodically check user permissions and remove access that is no longer necessary.
- Monitor and audit activity: Keep records of access attempts and user activity to identify unusual behavior or potential security issues.
- Update access when roles change: Promptly modify or revoke permissions when employees change roles or leave the organization.
Frequently Asked Questions
How often should access permissions be reviewed?
There is no definite timeline as to when and how often access permissions should be reviewed. But to ensure compliance with regulations like SOC2 or HIPAA, organizations are encouraged to review their access permissions quarterly and whenever there is a significant change in an employee’s role, responsibilities, or employment status.
What is the difference between authentication and access control?
Authentication is one component of access control and is used to verify who a user is, while access control determines what that authenticated user is allowed to access or do. For example, MFA may confirm a director’s identity, while role-based permissions determine which board documents that director can view.
Strengthen Your Business’s Cybersecurity with Convene Board Portal
Access control is one of the most important building blocks of modern security. It helps you protect sensitive systems and information by ensuring that access is granted deliberately and monitored consistently. More than a technical safeguard, access control also supports stronger governance. It helps leadership teams share confidential information securely, maintain accountability, and keep critical decisions moving without exposing the organization to unnecessary risk.
Convene Board Portal supports this by helping organizations strengthen access control through enterprise-grade security features, designed to protect sensitive information, including:
- Granular permission and document controls that allow role-based access for executives and administrators
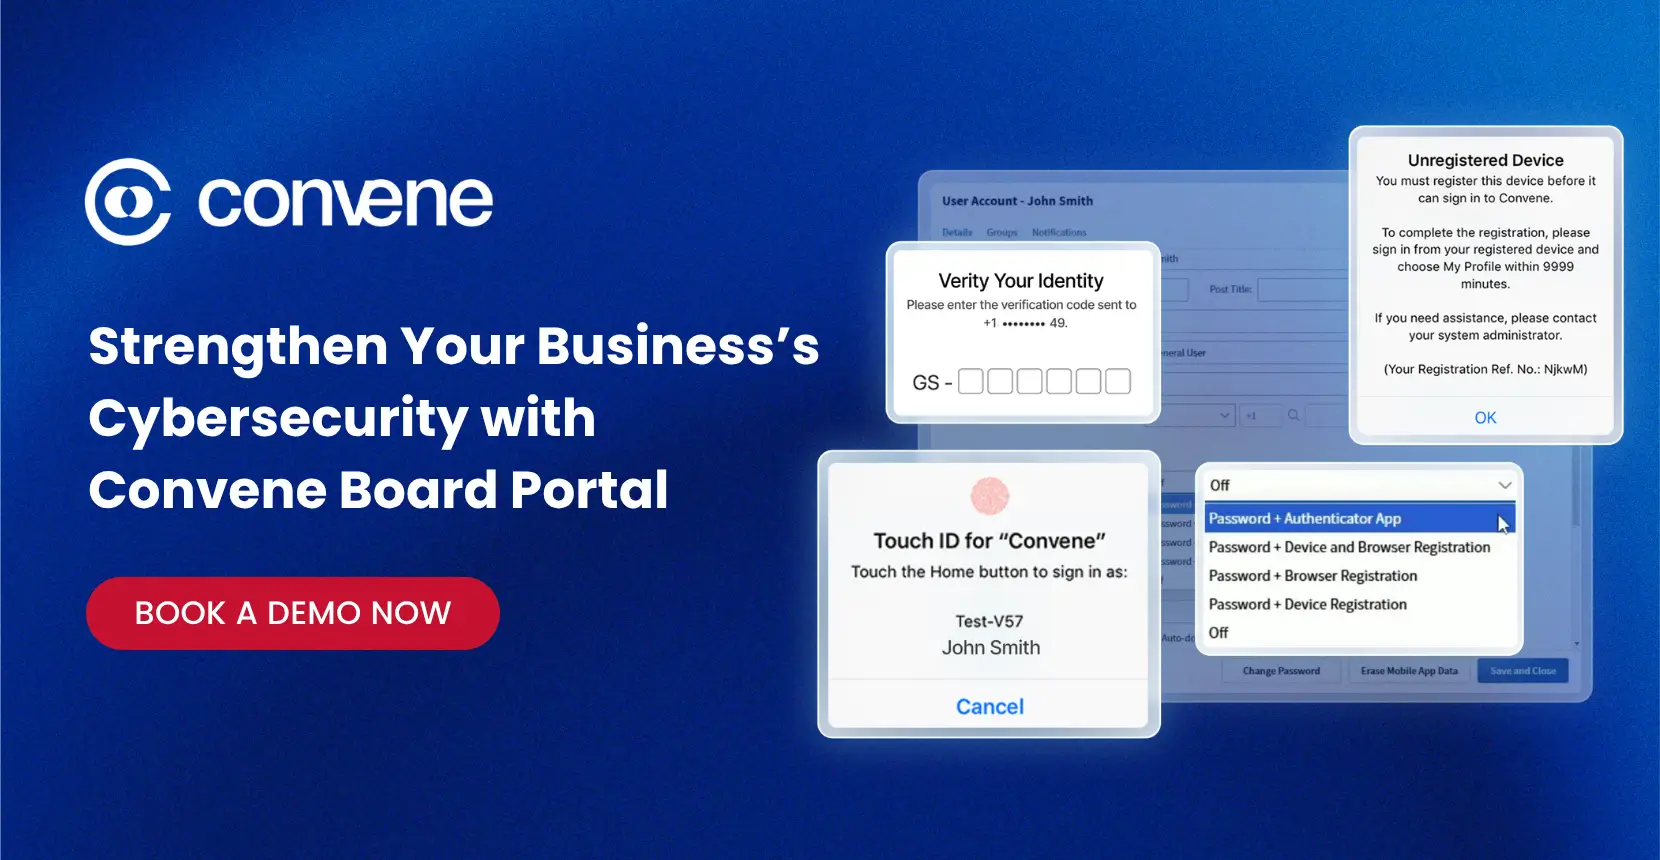
- Stronger authentication and account security with MFA, device registration, session timeout settings, and sign-in retry limits
- Data protection and accountability measures that provide multi-level encryption for data at rest and in transit, remote data wipe for lost or stolen devices, and audit-ready activity tracking
Together, these features support a safer and more efficient board meeting and governance.
Request a demo to see how Convene can support your organization’s governance and security.


Jess is a Content Marketing Writer at Convene who commits herself to creating relevant, easy-to-digest, and SEO-friendly content. Before writing articles on governance and board management, she worked as a creative copywriter for a paint company, where she developed a keen eye for detail and a passion for making complex information accessible and enjoyable for readers. In her free time, she’s absorbed in the most random things. Her recent obsession is watching gardening videos for hours and dreaming of someday having her own kitchen garden.
- Connect:
-